UNDER ATTACK RIGHT NOW? CALL (866) 908-8800 — 24/7 INCIDENT RESPONSE
First ResponseCyber Defense
Home Services Incident Response About Contact Call (866) 908-8800
Cybersecurity operator working in a darkened security operations room
24/7 Cyber Incident Response

When they strike.
We strike back.

A breach doesn't wait for business hours — and neither do we. First Response Cyber is the 24/7 emergency response and managed defense team for small and mid-sized businesses. We detect the attack, contain the damage, and get you back on your feet. Fast.

SOC MONITORING ACTIVE · HUMAN-LED · AI-ACCELERATED
$10.5T
Projected annual cost of cybercrime
Cybersecurity Ventures
46%
Of breaches hit businesses under 1,000 staff
Verizon DBIR
277d
Avg. days to identify & contain a breach
IBM
24/7
When we answer the phone & start response
First Response Cyber
Active incident

Under attack right now?

Ransomware on your screen. Accounts locked. Money moved. Don't pay, don't panic, don't power down. Call us — a responder picks up, 24/7.

The hard truth

Most tools tell you something happened. Then leave you to fix it.

Attackers moved past antivirus years ago. They buy their way in with stolen passwords, phishing, and tools that never trip an alarm. By the time a dashboard lights up, they've been inside for weeks. Small businesses are the target precisely because they're told they're "too small to matter."

01

Alert-only defense

An alert is not protection. A SIEM that pages you at 3 a.m. with a problem you can't contain is just an expensive smoke detector with no fire crew.

02

Nobody after 5 p.m.

Attacks are timed for nights, weekends and holidays — when your IT person is asleep. Defense that clocks out at 5 is defense the attacker plans around.

03

Minutes matter, hours lose

Modern ransomware can encrypt an entire network in under an hour. Identity attacks move in seconds. Response measured in days is a business-ending delay.

What we do

One team. The whole fight.

Prevention, detection, response and recovery — run as a single managed service, backed by our own security platform and a human team that actually acts.

How first response works

Detect. Respond. Contain. Recover.

The same discipline a fire crew brings to a burning building — applied to your network, around the clock.

1
Phase 01
// SECONDS

Detect

Human-led, AI-accelerated monitoring flags the real attack in the noise — across endpoints, cloud, email and identity.

2
Phase 02
// MINUTES

Respond

A responder takes command. We confirm the threat, pick up the phone, and act — no ticket queue, no hand-off.

3
Phase 03
// CONTAIN

Contain

Isolate infected machines, kill malicious sessions, lock compromised accounts. We stop the spread before it becomes a shutdown.

4
Phase 04
// RECOVER

Recover

Evict the attacker, restore operations, preserve the evidence, and harden what let them in — with a clear report you can hand to insurers.

Security analyst monitoring live code and alerts on dual screens// LIVE SOC
The difference

We act. We don't just alert.

Plenty of vendors will sell you a dashboard and a monthly report. When the alarm goes off, you're on your own. We built First Response Cyber to be the crew that shows up — the hands that actually contain the threat while you keep running your business.

  • A real human answers — 24 hours a day, every day
  • Active containment, not a ticket in a queue
  • One accountable team from detection to recovery
  • Flat, predictable pricing built for an SMB budget
Why we're different →
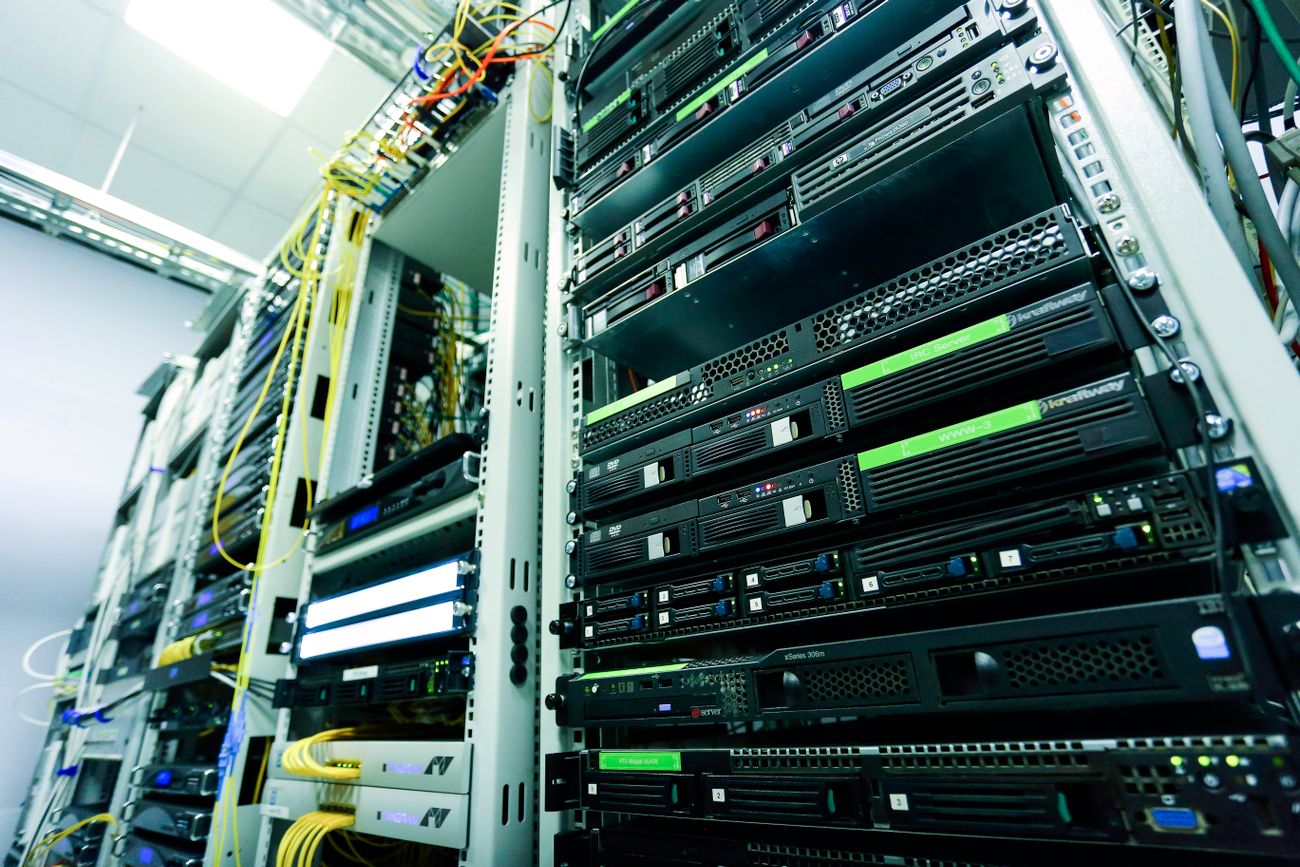
High-tech server racks in a secure data center// ARGOS PLATFORM
The engine room

Enterprise-grade. SMB-sized.

First Response Cyber runs on the Argos security platform — the same detection, response and threat-intelligence engine built and operated by our parent company, Intelligent Automation, to defend its own clients every day. You get the muscle of an enterprise SOC without hiring one.

  • Unified detection across endpoint, cloud, identity & email
  • Threat intelligence that updates defenses in near real time
  • Evidence and audit trails that stand up to insurers & regulators
  • Backed by Intelligent Automation, LLC — MSP & MSSP since day one
Meet the team behind it →
Powered & operated by Intelligent Automation, LLC The Argos Security Platform Human-Led SOC 24/7/365 Dispatch
Straight answers

The questions worth asking

What happens the moment I call? +
A responder — a real person, not a call-center script — picks up 24/7. We get the essentials, start containment guidance immediately, and stand up a response team. If you're an existing managed client, we're often already acting before you finish the call.
Do I have to be a customer to get emergency help? +
No. Our emergency incident-response line is open to any business under active attack. We'll help you contain and recover, then show you how to make sure it doesn't happen again. Call (866) 908-8800.
We already have antivirus and a firewall. Isn't that enough? +
Those are the locks on the doors — necessary, but attackers walk past them every day using stolen passwords and phishing. Managed detection and response adds the alarm system, the cameras and the response crew, watching 24/7 for what slips through.
Are you affordable for a small business? +
Yes — that's the whole point. We package enterprise-grade defense into flat, predictable monthly pricing sized for small and mid-sized budgets, with no setup fees and no long-term lock-in. Tell us your size and we'll scope it in a day.
Who actually runs First Response Cyber? +
We're a division of Intelligent Automation, LLC, a managed-services and cybersecurity company, operating on its Argos security platform. You get a focused emergency-response brand backed by an established security operation.
Don't wait for the breach

Get a crew on your side before you need one.

The cheapest incident is the one that never lands. Start with a free, no-pressure defense assessment — we'll show you exactly where you're exposed.